Protecting School Data in Ghana: Privacy, Security and Responsible Digital Management
Schools hold some of the most sensitive information in any community: children's names, health details, family contacts and results. What Ghana's Data Protection Act says, what may change, and practical steps on access, passwords, backups, messaging and breaches that any school can take.
In this article
This article explains good practice and summarises what Ghana's data protection law says. It is not legal advice. For decisions about your school's legal obligations, consult the Data Protection Commission or a qualified lawyer.
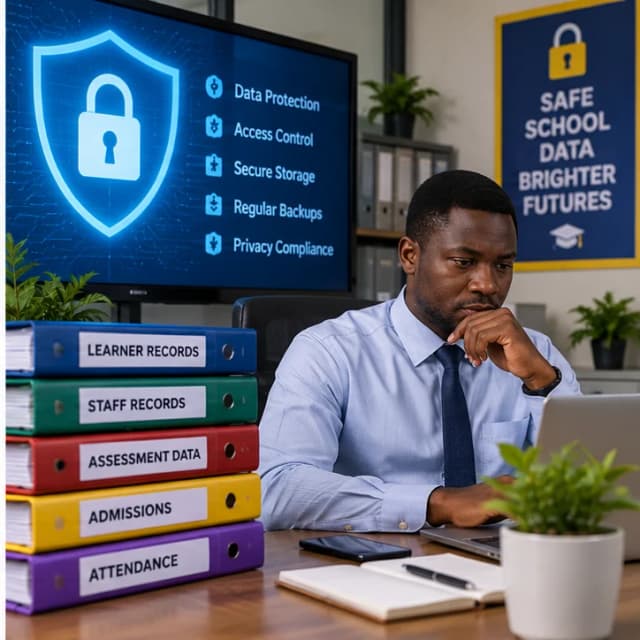
A typical basic school holds a remarkable amount of personal information. There are admission forms with dates of birth and home addresses, parents' phone numbers, health conditions and allergies, attendance registers, test scores, fee records, disciplinary notes and photographs. Not long ago, most of it lived in files and registers in the head teacher's office. Today it is also on laptops, phones, flash drives, cloud services and WhatsApp groups. Every one of those places is somewhere it can be lost, stolen or shared by mistake. Protecting it is a matter of trust between a school and its families, of children's safety, and of law.
What Ghana's law says
The Data Protection Act, 2012 (Act 843)
Ghana's main data protection law is the Data Protection Act, 2012 (Act 843), which established the Data Protection Commission. Several of its provisions are directly relevant to schools.
Eight principles. Section 17 requires anyone who processes personal data to take the individual's privacy into account by applying eight principles: accountability, lawfulness of processing, specification of purpose, compatibility of further processing with the purpose of collection, quality of information, openness, data security safeguards, and data subject participation.
Only what is needed. Under section 19, personal data may only be processed if the purpose is "necessary, relevant and not excessive".
A clear purpose. Sections 22 and 23 require data to be collected for a purpose that is "specific, explicitly defined and lawful", and require the person collecting it to make sure the individual is aware of that purpose.
Consent and its exceptions. Section 20 states that personal data shall not be processed without the prior consent of the data subject, unless the processing is necessary for a contract, authorised or required by law, needed to protect the data subject's legitimate interest, necessary for a statutory duty, or necessary to pursue a legitimate interest of the data controller or a third party.
Children's data. Section 37 treats personal data relating to "a child who is under parental control in accordance with the law" as special personal data, alongside information such as health and religious beliefs. Such data may be processed where the processing is necessary or the data subject consents.
Pupils' records. Section 62 provides that personal data held by an educational institution that relates to a pupil at the institution "shall not be disclosed except where the disclosure is required by law".
Keeping data no longer than necessary. Section 24 says personal data should not be retained longer than necessary for its purpose, subject to exceptions such as where the law requires it, and that records should then be destroyed, deleted or de-identified.
Security. Section 28 requires data controllers to adopt "appropriate, reasonable, technical and organisational measures" to prevent loss, damage, unauthorised destruction and unlawful access. This includes identifying foreseeable risks, putting safeguards in place, checking that they work, and updating them.
Breaches. Under section 31, where there are reasonable grounds to believe that personal data has been accessed or acquired by an unauthorised person, the data controller must notify the Commission and the data subject "as soon as reasonably practicable".
Registration. Section 27 requires a data controller who intends to process personal data to register with the Commission. The Commission's website explains registration.
How these provisions apply to a particular school, including which of the consent exceptions apply and what registration requires, is a question for the Commission or a lawyer. The Act also contains specific exemptions relating to examination marks and examination scripts (sections 72 and 73), which schools should seek advice on rather than interpret alone.
What may change
The law is under review. A draft Data Protection Bill, 2025 is published on the Commission's website. Among other things, the draft would repeal Act 843, establish a Data Protection Authority in place of the Commission, require a data controller to obtain a parent's or legal guardian's consent before processing a child's personal data unless the processing is permitted or required by law, and require breaches to be notified "immediately or within 72 hours" of discovery. In March 2026 the government said it was developing a new Data Protection Bill. At the time of writing, the draft is not law, and its provisions may change before it is passed. Schools should check the current position before relying on it.
Practical steps any school can take
The law sets the expectations. The steps below are good practice that helps a school meet them, whatever its size or budget.
1. Collect less
Look at your admission form and ask of every question: what do we use this for? If the answer is "nothing", stop asking. Information you never collect can never leak. Take particular care with categories the Act treats as special, such as health and religious beliefs: collect them only where there is a clear need, such as recording a learner's allergy so staff can respond in an emergency.
2. Give people access only to what they need
Not everyone in a school needs to see everything. A class teacher needs their own class's records. The bursar needs fee records but not health information. The head teacher may need an overview of all of it. Whether records are on paper or in software, set access by role, and remove access promptly when a staff member leaves or changes role. Never share one login between several people: if something goes wrong, nobody can tell who did what.
3. Use better passwords, not more complicated ones
Modern guidance has moved away from short, complicated passwords that must be changed every few months. The US National Institute of Standards and Technology, whose guidance is widely followed, now requires passwords used on their own to be at least 15 characters long. It says systems should not impose composition rules, such as demanding a mixture of character types, and should not force people to change passwords periodically unless there is evidence of compromise. It also says systems should block commonly used or compromised passwords and allow password managers (NIST, 2025).
In practice, that means a long passphrase made of several unrelated words, a different password for every important account, and a password manager to remember them. Where a service offers a second step at sign-in, such as a code sent to a phone, turn it on.
4. Secure devices and paper
Lock computers and phones with a PIN or password, and set them to lock automatically. Keep paper files containing personal information in a locked cabinet, and don't leave registers or report books where visitors can read them. Before disposing of an old computer or phone, wipe it properly. Avoid carrying learner records around on unencrypted flash drives, which are easy to lose.
5. Be careful with WhatsApp and social media
Messaging apps are now part of school life, but they are easy to misuse. Never post a list of learners' results, or of families who owe fees, in a class or parents' group. Share that information with each family privately. Before posting photographs of children on social media, seek parents' permission, avoid pairing photographs with full names, and consider whether the image reveals more than intended, such as a uniform, a location or a timetable.
6. Back up, and test the backup
A fire, a theft, a failed hard drive or ransomware can destroy records in an instant. The UK National Cyber Security Centre advises organisations to identify the data they could not function without, to back it up regularly, to keep backups in a different location (cloud storage is a cost-effective option), to keep the backup device from being permanently connected to the computer holding the original, and to make sure backups are recent and can actually be restored (NCSC, 2020). A backup that has never been tested is a hope, not a plan.
7. Choose software providers carefully
When a school uses a school management system or any cloud service, the provider processes data on the school's behalf. The Act expects such a processor to act only with the data controller's authorisation, to treat the data as confidential and to apply security measures (sections 29 and 30). Before signing up, ask the provider:
Where is the data stored, and who can access it?
How is it protected, and how often is it backed up?
Can the school export all of its data, and will the provider delete it if the school leaves?
How, and how quickly, will the school be told if there is a breach?
8. Keep records only as long as needed
Agree how long each kind of record is kept, in line with any legal or Ghana Education Service requirements, and dispose of the rest securely: shred paper and delete files properly, including from backups and shared folders.
9. Prepare for something going wrong
Decide in advance who does what if data is lost, stolen or sent to the wrong person: who is told first, how the damage is limited, how the facts are recorded, and how the school will notify the Data Protection Commission and the people affected, as section 31 requires. The Commission's website has a page for reporting a breach.
A short checklist
We know what personal data we hold, where it is, and why we hold it.
Our forms collect only what we use.
Staff can see only the records their role requires, and leavers lose access.
Important accounts use long, unique passphrases, and a second sign-in step where available.
Devices lock automatically, and paper records are locked away.
No results, fee lists or other personal information are posted in group chats.
We ask parents before publishing photographs of children.
Backups are automatic, stored separately, and tested.
We know what our software providers do with our data.
We have a plan for data breaches, including notifying the Commission.
Conclusion
Protecting school data is not mainly a technical problem. Most of it comes down to habits: collecting less, sharing carefully, locking things away, backing up and knowing what to do when something goes wrong. Software can help, and the next generation of school management systems will make some of these habits easier, but no system can protect information that staff post in the wrong group chat. Families entrust schools with their children every day. Their children's information deserves the same care.
Try this week: With one colleague, list every place your school keeps learners' personal information: files, registers, laptops, phones, flash drives, cloud accounts and messaging groups. Next to each, write who can access it. That single page will show you where to start.
Disclosure: MosTek Solutions develops school management software. This article does not recommend any particular product.
References
Data Protection Act, 2012 (Act 843). Republic of Ghana. Official PDF via the Data Protection Commission
Data Protection Bill, 2025 (draft). Republic of Ghana. PDF via the Data Protection Commission
Data Protection Commission, Ghana. dpc.gov.gh
Ghana News Agency (2 March 2026). Govt to introduce new Data Protection Bill to regulate AI, cross-border data flows. gna.org.gh
National Cyber Security Centre (2020). Cyber Security Small Business Guide (version 4). PDF
National Institute of Standards and Technology (2025). Digital Identity Guidelines: Authentication and Authenticator Management (SP 800-63B-4). pages.nist.gov
About the author
Moses Bentum
Moses Bentum is a Ghanaian educator, software developer, and founder of MosTek Solutions. With a background in Science Education and Information Technology, he develops innovative software solutions for schools and businesses. His interests include artificial intelligence, educational technology, data analytics, and digital transformation. Through MosTek Insights, he shares practical knowledge, research perspectives, and technology-driven solutions.
More from Moses Bentum